BruCON 0x11: Volunteering at Belgium’s Biggest Hacker Conference
A few weeks ago I spent five days in Mechelen as part of the staff team at BruCON 0x11, and I’m still buzzing about it. I wanted to write this up partly to share what the conference is actually like for anyone who hasn’t been, and partly because being on the other side of an event like this, as a volunteer rather than just an attendee, completely changed how I see these conferences.
What is BruCON?
BruCON is an annual security and hacker conference providing two days of an interesting atmosphere for open discussions of critical infosec issues, privacy, information technology and its cultural and technical implications on society. It’s been running since 2009 and is widely considered one of the most important gatherings of the hacker and security community in Europe.
What makes it different from the bigger corporate conferences is the philosophy. It’s a conference by and for the security and hacker community. The organizers deliberately try to build bridges between everyone working in security: hackers, security professionals, security communities, non-profit organizations, CERTs, students, and law enforcement agencies. You end up in hallway conversations with people whose careers span every corner of the field.
This year was BruCON 0x11, the 17th edition (the hex numbering is very on-brand for a hacker con). It ran from 22 to 26 September 2025, with hands-on training from the 22nd to the 24th and the two-day main conference on the 25th and 26th.
The Venue
BruCON took place in Mechelen, a small city between Brussels and Antwerp that turns out to be the perfect setting for this kind of event. The main venue was Lamot Mechelen, which hosts the talks, workshops, and some of the training sessions. It’s a converted historic brewery right on the water, which fits a conference whose unofficial hashtag is #HackingForBeer.
The city itself is compact enough that everything is walkable, which matters more than you’d think when you’re running between sessions and trying to grab food. The whole thing had a relaxed, community feel rather than the sprawling convention-center energy of larger events.
The Scale
This year drew around 600 visitors from all over the world. That number is worth dwelling on, because 600 is a sweet spot. It’s big enough to pull world-class speakers and a genuinely international crowd, but small enough that you actually keep running into the same people and building real connections over the few days. By day two I was recognizing faces and having follow-up conversations that started in a talk the day before.
One write-up I read afterward from a team that attended captured it perfectly: enthusiasts from all over the world, spontaneous discussions in the corridors, and smooth organization that left plenty of room for exchange. And this part stuck with me. BruCON is above all a community. There are no glittery badges or flashy marketing, just people who love to understand, break down, rebuild and share.
The Content
The technical program was the real draw. The keynote this year set the tone for where the whole industry’s head is at: Sebastien Deleersnyder opened with “Secure with AI or Despite AI,” looking at how the security industry and the hacker community will adapt to AI’s expanding influence. 2025 really was the year that AI moved from a side topic to the thing everyone was talking about, and BruCON reflected that.
Beyond the keynote, the talks covered an enormous range: advanced WiFi attacks using everyday hardware, automated binary analysis using Ghidra’s P-Code intermediate language, techniques to bypass Microsoft Defender for Identity across the kill chain in on-premises Active Directory environments, and red and blue team operations using tools like Caldera. As someone who spends a lot of time in Active Directory and offensive tooling, the Defender for Identity bypass talk was exactly my kind of session.
The training side was just as strong. The spring and conference training tracks included courses like “AI SecureOps: Attacking and Defending GenAI Applications” by Abhinav Singh, the Corelan expert-level stack-based exploitation class by Peter Van Eeckhoutte, and “Mastering Advanced Incident Response in the Microsoft Cloud.” These are the kind of deep, multi-day courses you normally only get at the most established conferences.
And of course there was the CTF. The online Capture the Flag starts on the first day of the conference and runs until Friday afternoon, with winners and prizes revealed during the closing talk. There was even a 10km run on day two, with everyone meeting at the Novotel entrance at 7:30 AM. I did not do the run. I had earned my sleep by that point. 
Being on Staff
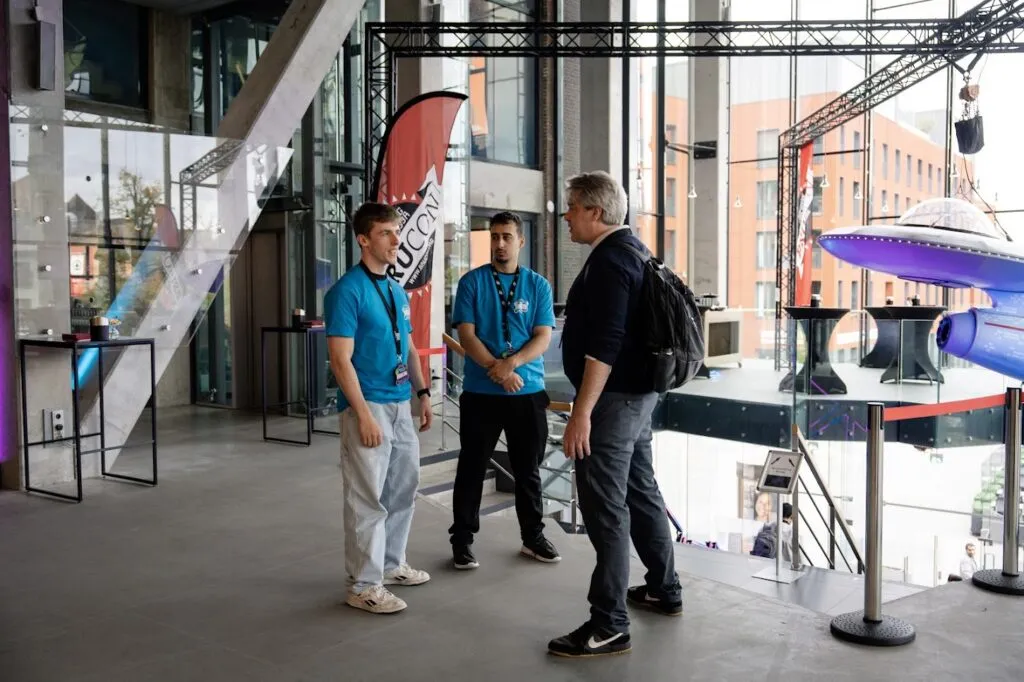
Here’s the part I really wanted to write about. I wasn’t just there as an attendee, I was part of the volunteer staff team, and that experience was the highlight of the whole week for me.
Volunteering at a conference like this means you see all the machinery that makes the event feel effortless from the outside. The “smooth organization” that everyone praises in their write-ups doesn’t just happen. It’s a team of people running registration, helping speakers get set up, managing rooms, pointing lost attendees in the right direction, keeping sessions on schedule, and solving the hundred small problems that come up every hour. Being part of that gave me a completely new respect for everyone who organizes these events.
It also turned out to be the best possible way to experience BruCON. As staff you’re constantly talking to people: speakers, attendees, other volunteers from all over Europe. By the end I’d had conversations I never would have had as a regular attendee hovering at the edge of the crowd. The volunteer team itself was incredible: a mix of students, professionals, and longtime community members who all showed up because they care about the event. That sense of everyone pulling together for something they believe in is exactly the community spirit BruCON is known for, just seen from the inside.
I learned a lot of practical things too: how a conference of this size actually runs, how to handle the inevitable last-minute chaos calmly, how much coordination goes into something that looks simple. Those are skills that go well beyond security.
Why It Mattered to Me
As a student getting deeper into offensive security, being in a room with 600 people who live and breathe this field was genuinely motivating. The talks pushed me to look into areas I hadn’t explored, the hallway conversations gave me ideas and contacts, and being on staff showed me that contributing to the community is just as rewarding as consuming its content.
One of the attending teams summed up their experience by saying this edition would remain a highlight of their 2025. I feel exactly the same way, and I got to experience it from behind the scenes.
If you’re a student in security and you ever get the chance to volunteer at a conference like BruCON, take it without hesitation. You’ll see the event in a way most attendees never will, you’ll meet people you’d otherwise never talk to, and you’ll come away with a much deeper appreciation for the community that makes all of this possible.
Already looking forward to the next one. 🍻 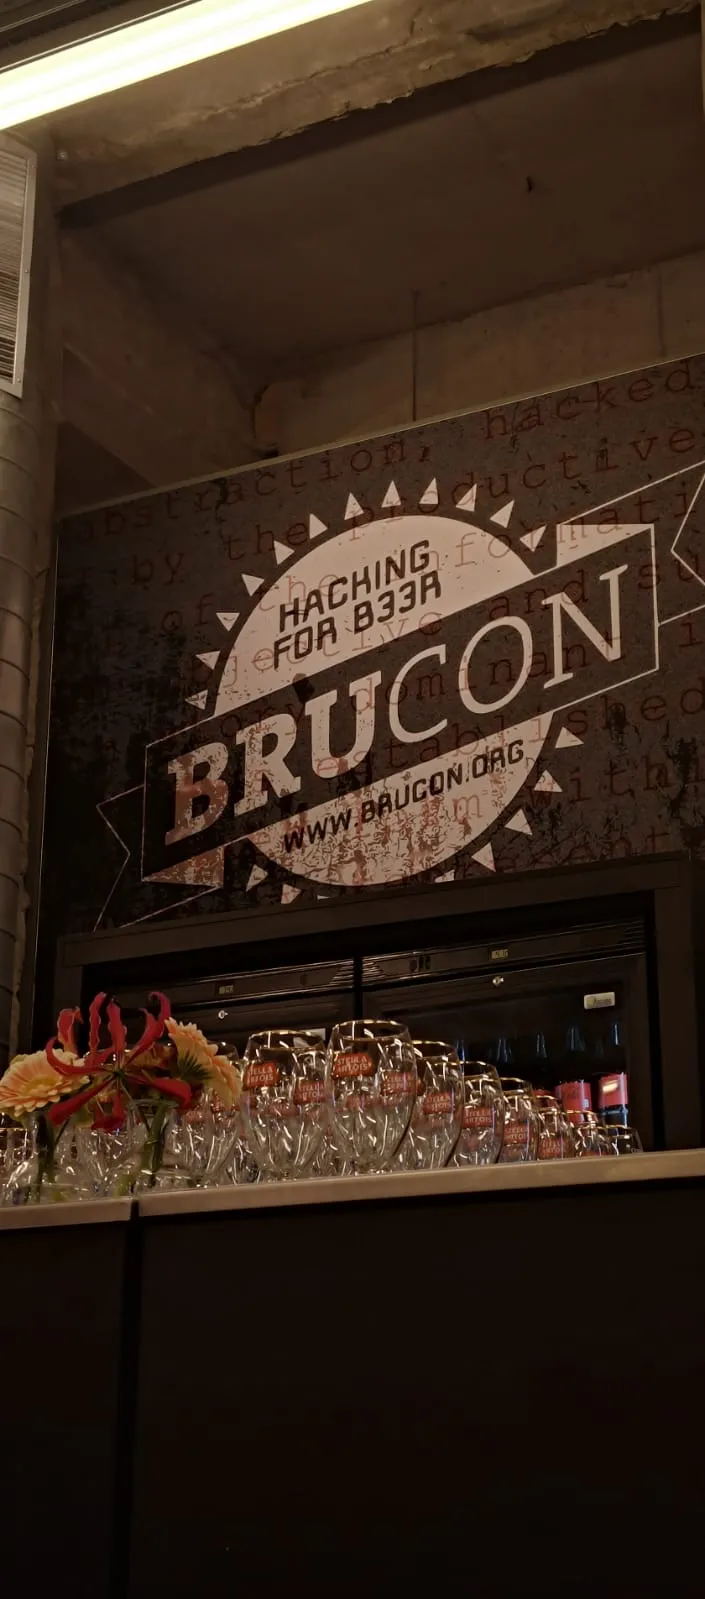
BruCON 0x11 took place 22–26 September 2025 at Lamot in Mechelen, Belgium. You can find more about the conference and recordings of past talks at brucon.org.